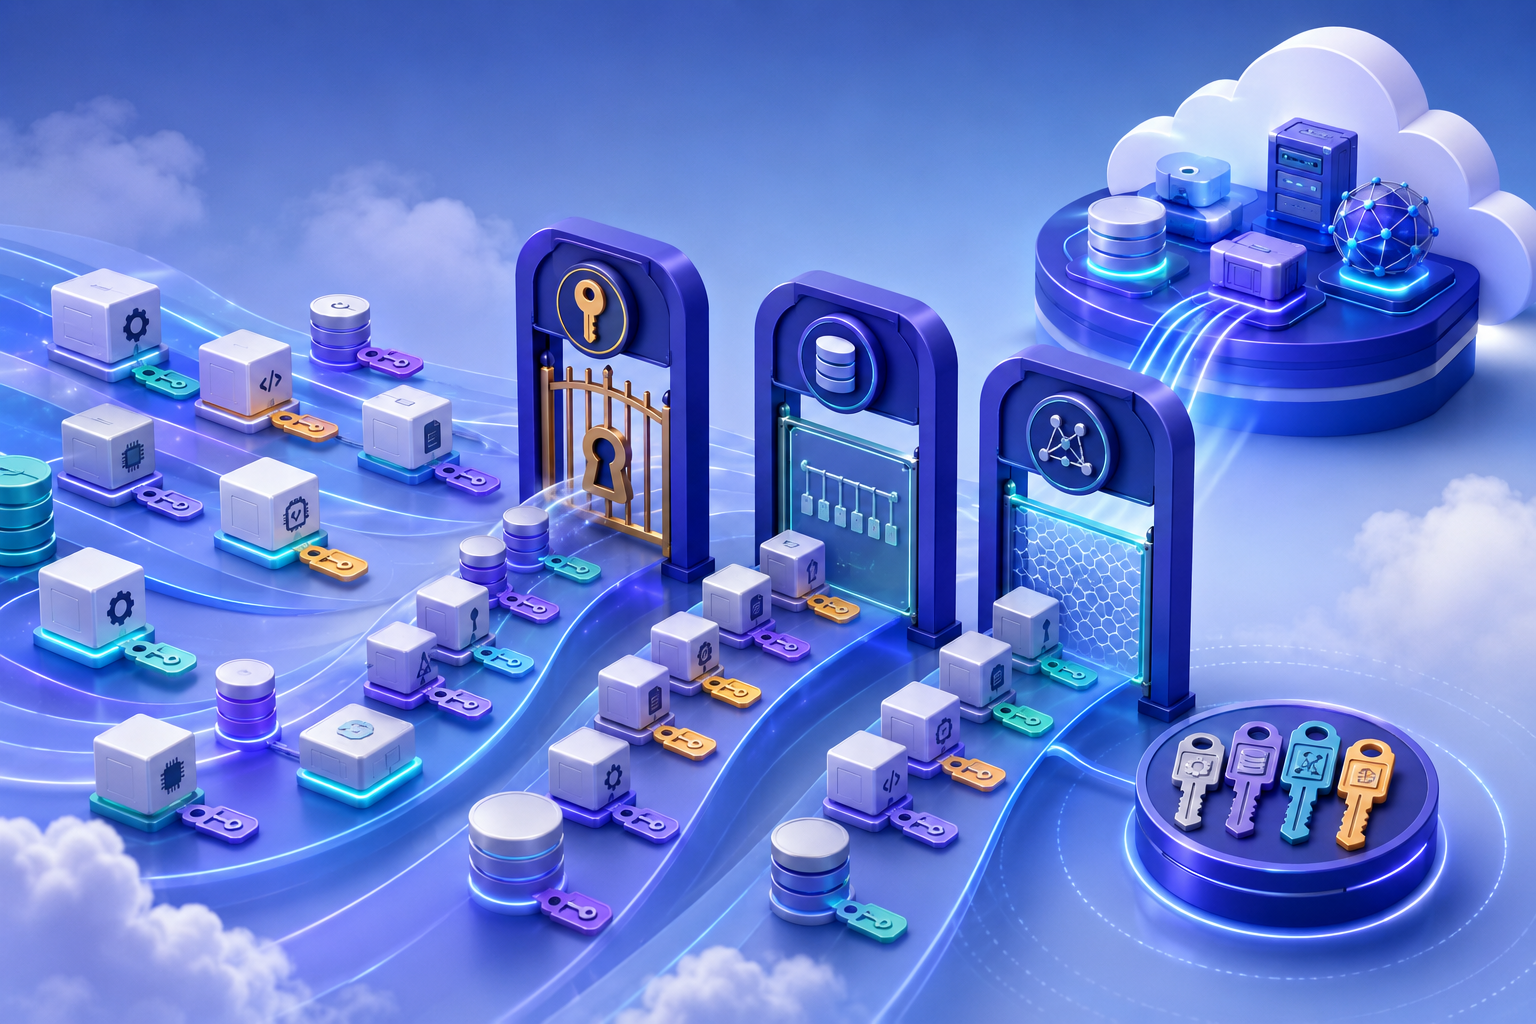
The Principle of Least Privilege: Why Less Access Means Better Security
Imagine you have an application that only needs to read files from a cloud storage bucket. Would you give it permission to delete those files, create new buckets, or manage permissions across your entire cloud account? Probably not. Yet granting applications, services, and users more permissions than they need is a common security mistake.
This is exactly what the Principle of Least Privilege (PoLP) aims to prevent.
What Does It Mean?
The principle states that a user, application, or system should only have the permissions necessary to perform its intended tasks.
Think of it like giving someone a key to your house. If a person only needs access to your garden, there's no reason to give them a key that opens every room in your house. The same idea applies to software systems. If an application only needs to read data from a database, it shouldn't have permission to modify or delete that data.
The goal is simple: Give access to what is needed, and restrict everything else.
Why Does It Matter?
Following this principle offers several benefits beyond simply adopting a security best practice.
1. It Limits the Impact of Security Breaches
Imagine an attacker steals the credentials of a service that reads customer information. If the service has read-only access to a specific database, the attacker may be able to read that data, but those credentials won't allow them to modify or delete it. Now imagine that the same service has administrator permissions. The attacker could potentially modify records, delete databases, or perform other destructive operations.
The initial compromise is the same, but the potential damage is very different. Limiting permissions reduces what an attacker can do with compromised access.
2. It Protects Against Accidental Mistakes
Not every incident is caused by an attacker. Sometimes developers make mistakes, applications have bugs, or automation scripts behave unexpectedly.
Imagine a cleanup script intended to remove temporary files. If it only has permission to delete files within a designated temporary directory, an error is less likely to affect unrelated files. But if it has unrestricted access to the entire storage system, a small programming mistake could have much larger consequences.
Restricting permissions protects systems from unintended actions, not just malicious ones.
3. It Makes Access Easier to Understand and Audit
When applications and users have broad permissions, answering basic security questions becomes difficult:
Which services can modify customer data?
Who can delete production resources?
Which applications have access to sensitive information?
With well-defined permissions, these questions become easier to answer. This approach encourages teams to think explicitly about what each component needs access to, making security reviews and audits more manageable.
Real-World Examples
Here are a few examples of how this principle applies to everyday software engineering:
Database access: An analytics service that only generates reports should have read-only access to the necessary tables rather than full database administration privileges.
Cloud storage: An application that uploads images to one storage bucket shouldn't automatically have access to every bucket in the account.
CI/CD pipelines: A deployment pipeline should have permissions to deploy the required resources, rather than unrestricted administrative access to the entire cloud account.
Human access: A developer may need permission to inspect production logs without needing permission to modify production infrastructure.
API permissions: An integration that only reads a user's calendar should request read access rather than permission to create, modify, and delete events.
The common theme is that permissions should reflect responsibilities.
Why Is It Easier Said Than Done?
Because it's often easier to grant broad permissions than to figure out exactly what's needed.
Imagine you're building an MVP. Your priority is getting things working and shipping quickly, not spending time configuring permissions. You might connect your application to a database using an administrator account simply because it's already available and works out of the box. Or you might grant a service broad access to cloud resources to avoid running into permission errors.
These shortcuts save time initially, but permissions granted for convenience can easily make their way into production and remain there. That's one reason the principle is easy to understand but harder to put into practice.
How to Put It Into Practice
The key is to make least privilege a habit, even when building something small. A few practical steps can help:
Avoid administrator access by default. Create dedicated users or roles for your applications.
Start with limited permissions. Add more only when there's a legitimate need.
Use separate credentials for different purposes. For example, your application shouldn't need the same database permissions as your migration scripts.
Review permissions before going to production. Development shortcuts shouldn't automatically become production configurations.
Revisit permissions periodically. As applications evolve, remove access that is no longer needed.
You don't have to get everything perfect from the beginning. Being intentional about permissions goes a long way. It helps you build more secure systems, prepares your application for production, and sets you apart as a developer who takes security seriously. You can always refine permissions as your application evolves.
Final Thoughts
The Principle of Least Privilege is a simple idea with significant implications for software security. By limiting permissions to what users, applications, and services actually need, we reduce the potential impact of security breaches and accidental mistakes.
It's not a guarantee that nothing will go wrong. It's a way to make sure that when something does go wrong, the consequences are more contained.
Good security isn't always about adding more protection. Sometimes, it's about granting less access.